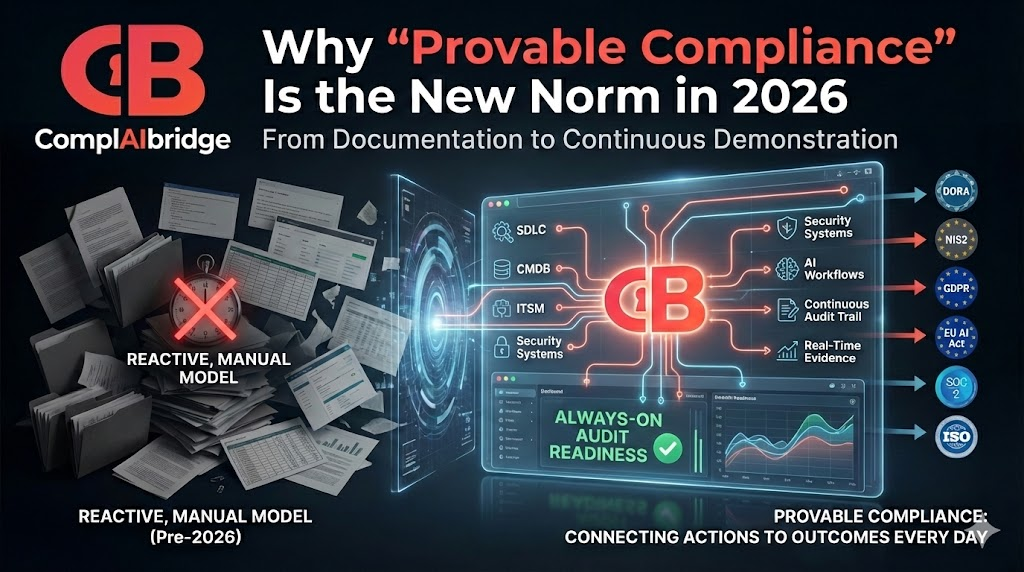
For decades, compliance was treated as a documentation exercise. Policies were written, controls were listed, evidence was collected, and audits were passed. If an organisation could produce the right paperwork at the right time, it was considered compliant.
In 2026, that model is officially broken.
Today, regulators, customers, and partners don't just want to know if you are compliant. They want to know how you stayed compliant, when key decisions were made, who approved them, and what actions were taken in response to risk. Compliance is no longer something you can assert at the end of a process. It's something you're expected to demonstrate continuously.
This shift is being driven by tightening regulations, continuous delivery, cloud-native systems, and the rise of AI-driven workflows. Frameworks like DORA, NIS2, GDPR, the EU AI Act, SOC 2, and sector-specific standards increasingly emphasise accountability, traceability, and auditability across the full system lifecycle. Regulators aren't just checking outputs anymore; they're scrutinising the path that led to those outcomes.
Yet most organisations are still running compliance on a reactive, manual model. Evidence is collected weeks before an audit. Screenshots are pulled from multiple tools. Spreadsheets are stitched together into audit packs. Security incidents are tracked separately from compliance controls. Vulnerabilities are prioritised without business or regulatory context. When something goes wrong, teams struggle to answer basic questions about why a control was implemented a certain way, who approved an exception, when a vulnerability was identified, or how remediation actions map to regulatory obligations.
That gap between operational activity and provable evidence is exactly what regulators are now focusing on.
Provable compliance isn't about producing more reports or adding more checklists. It's about connecting actions to outcomes. It means controls are mapped to requirements from the start, risks are identified early, and evidence is generated automatically as work happens. Security alerts and vulnerabilities are tied to compliance controls. Remediation actions are logged and traceable. Audit trails are continuous rather than reconstructed under pressure.
In this model, teams don't scramble to prove compliance at the end. They operate in a state of always-on audit readiness.
See it in action
See how ComplAIbridge fits your stack
Book a 20-minute walkthrough - no deck, no sales cycle, just the product.
Book a DemoThis is where platforms like Complaibridge are changing how compliance actually works in practice. Instead of replacing existing tools, Complaibridge connects an organisation's SDLC, CMDB, ITSM, and security systems into a single compliance engine. Using agentic AI and COAR (Compliance Orchestration, Automation & Response), it orchestrates workflows, automates evidence capture, and maintains a continuous audit trail across the entire Build-Run-Assure lifecycle.
In real terms, that means requirements, designs, builds, and tests are mapped to frameworks like ISO, SOC 2, DORA, NIS2, PCI, GDPR, and internal policies from day one. Security alerts, vulnerabilities, and incidents are continuously correlated with business impact and regulatory controls. Evidence is collected automatically from existing tools as work happens. Audit packs and Trust Centre views can be generated on demand. Every alert, decision, and remediation step is traceable without manual documentation.
Instead of compliance being a periodic event, it becomes a built-in operational capability.
Several forces are converging to make 2026 a tipping point. Regulators are raising the bar from point-in-time checks to lifecycle accountability. AI systems are increasing the need for explainability, decision traceability, and continuous monitoring. Enterprise customers are asking harder questions about security and compliance posture before signing contracts. And the operational cost of delayed remediation, compliance failures, and regulatory penalties is higher than ever.
Together, these trends make provable compliance not a competitive advantage, but a baseline expectation.
In 2026, the question won't be, "Are you compliant?" It will be, "Can you prove it right now?"
The organisations that win in regulated environments will be the ones that stop treating compliance as a reporting exercise and start engineering it into how they build, run, and assure their systems. Because in the new regulatory reality, compliance isn't something you prepare for once a year. It's something you demonstrate every day.
Keep reading
 Insights
Speed in Compliance: Why Faster Isn't Always Better
We celebrate speed everywhere. But in compliance, speed tells a very different story.
 Insights
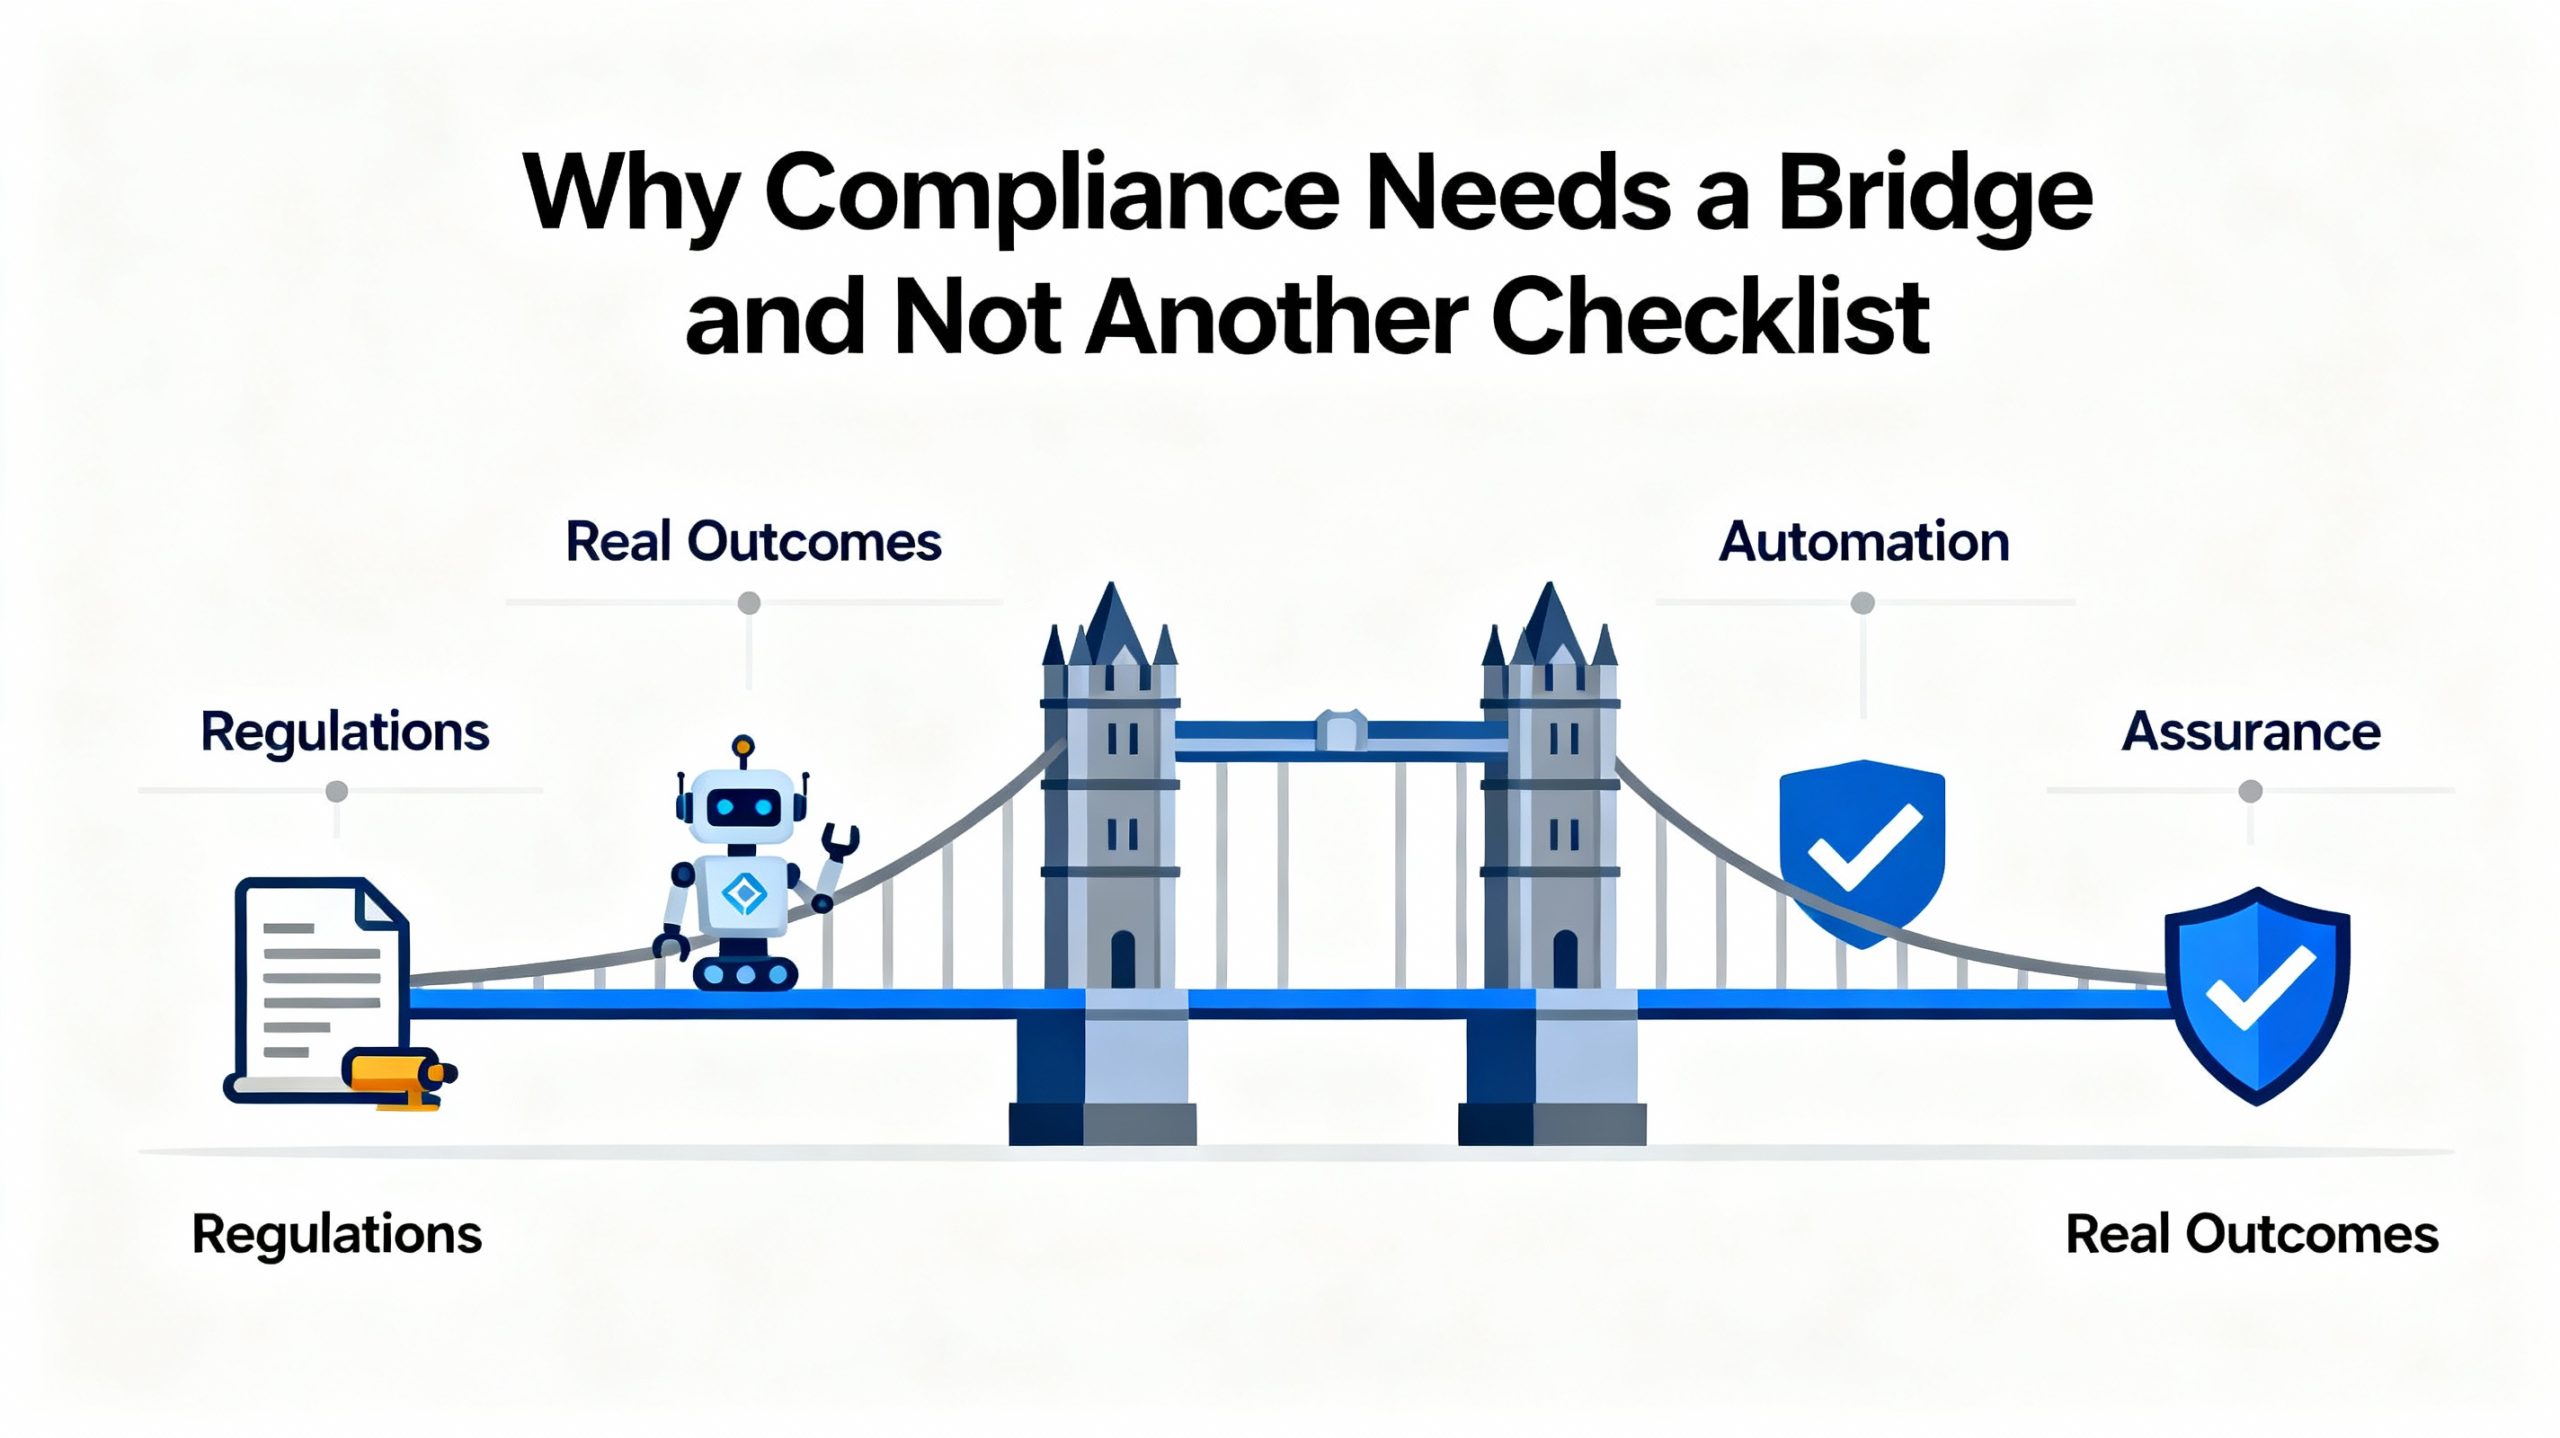
Why Compliance needs a bridge and not another checklist
Even today, for most organizations, compliance still feels like a never-ending loop of forms, audits, and documentation.
Get Early Access
Ready to make compliance
part of how you build?
Get in touch and we'll show you exactly how ComplAIbridge fits your stack, your team, and your frameworks.
No deck. No sales cycle. Just the product.