Blog
Insights on compliance,
AI, and how teams build.
Field notes on shipping compliant software, from classic SDLC to AI-native pipelines.
 Insights
Speed in Compliance: Why Faster Isn't Always Better
We celebrate speed everywhere. But in compliance, speed tells a very different story.
 Product
DevGovOps in Practice: How Complaibridge Makes It Work
DevGovOps is easy to agree with in principle. The challenge begins when this idea meets reality.
 Engineering
DevGovOps: The Missing Layer in Modern Software Delivery
DevSecOps brought security into the development lifecycle. It took a decade and it changed everything. Governance is next.
 Compliance
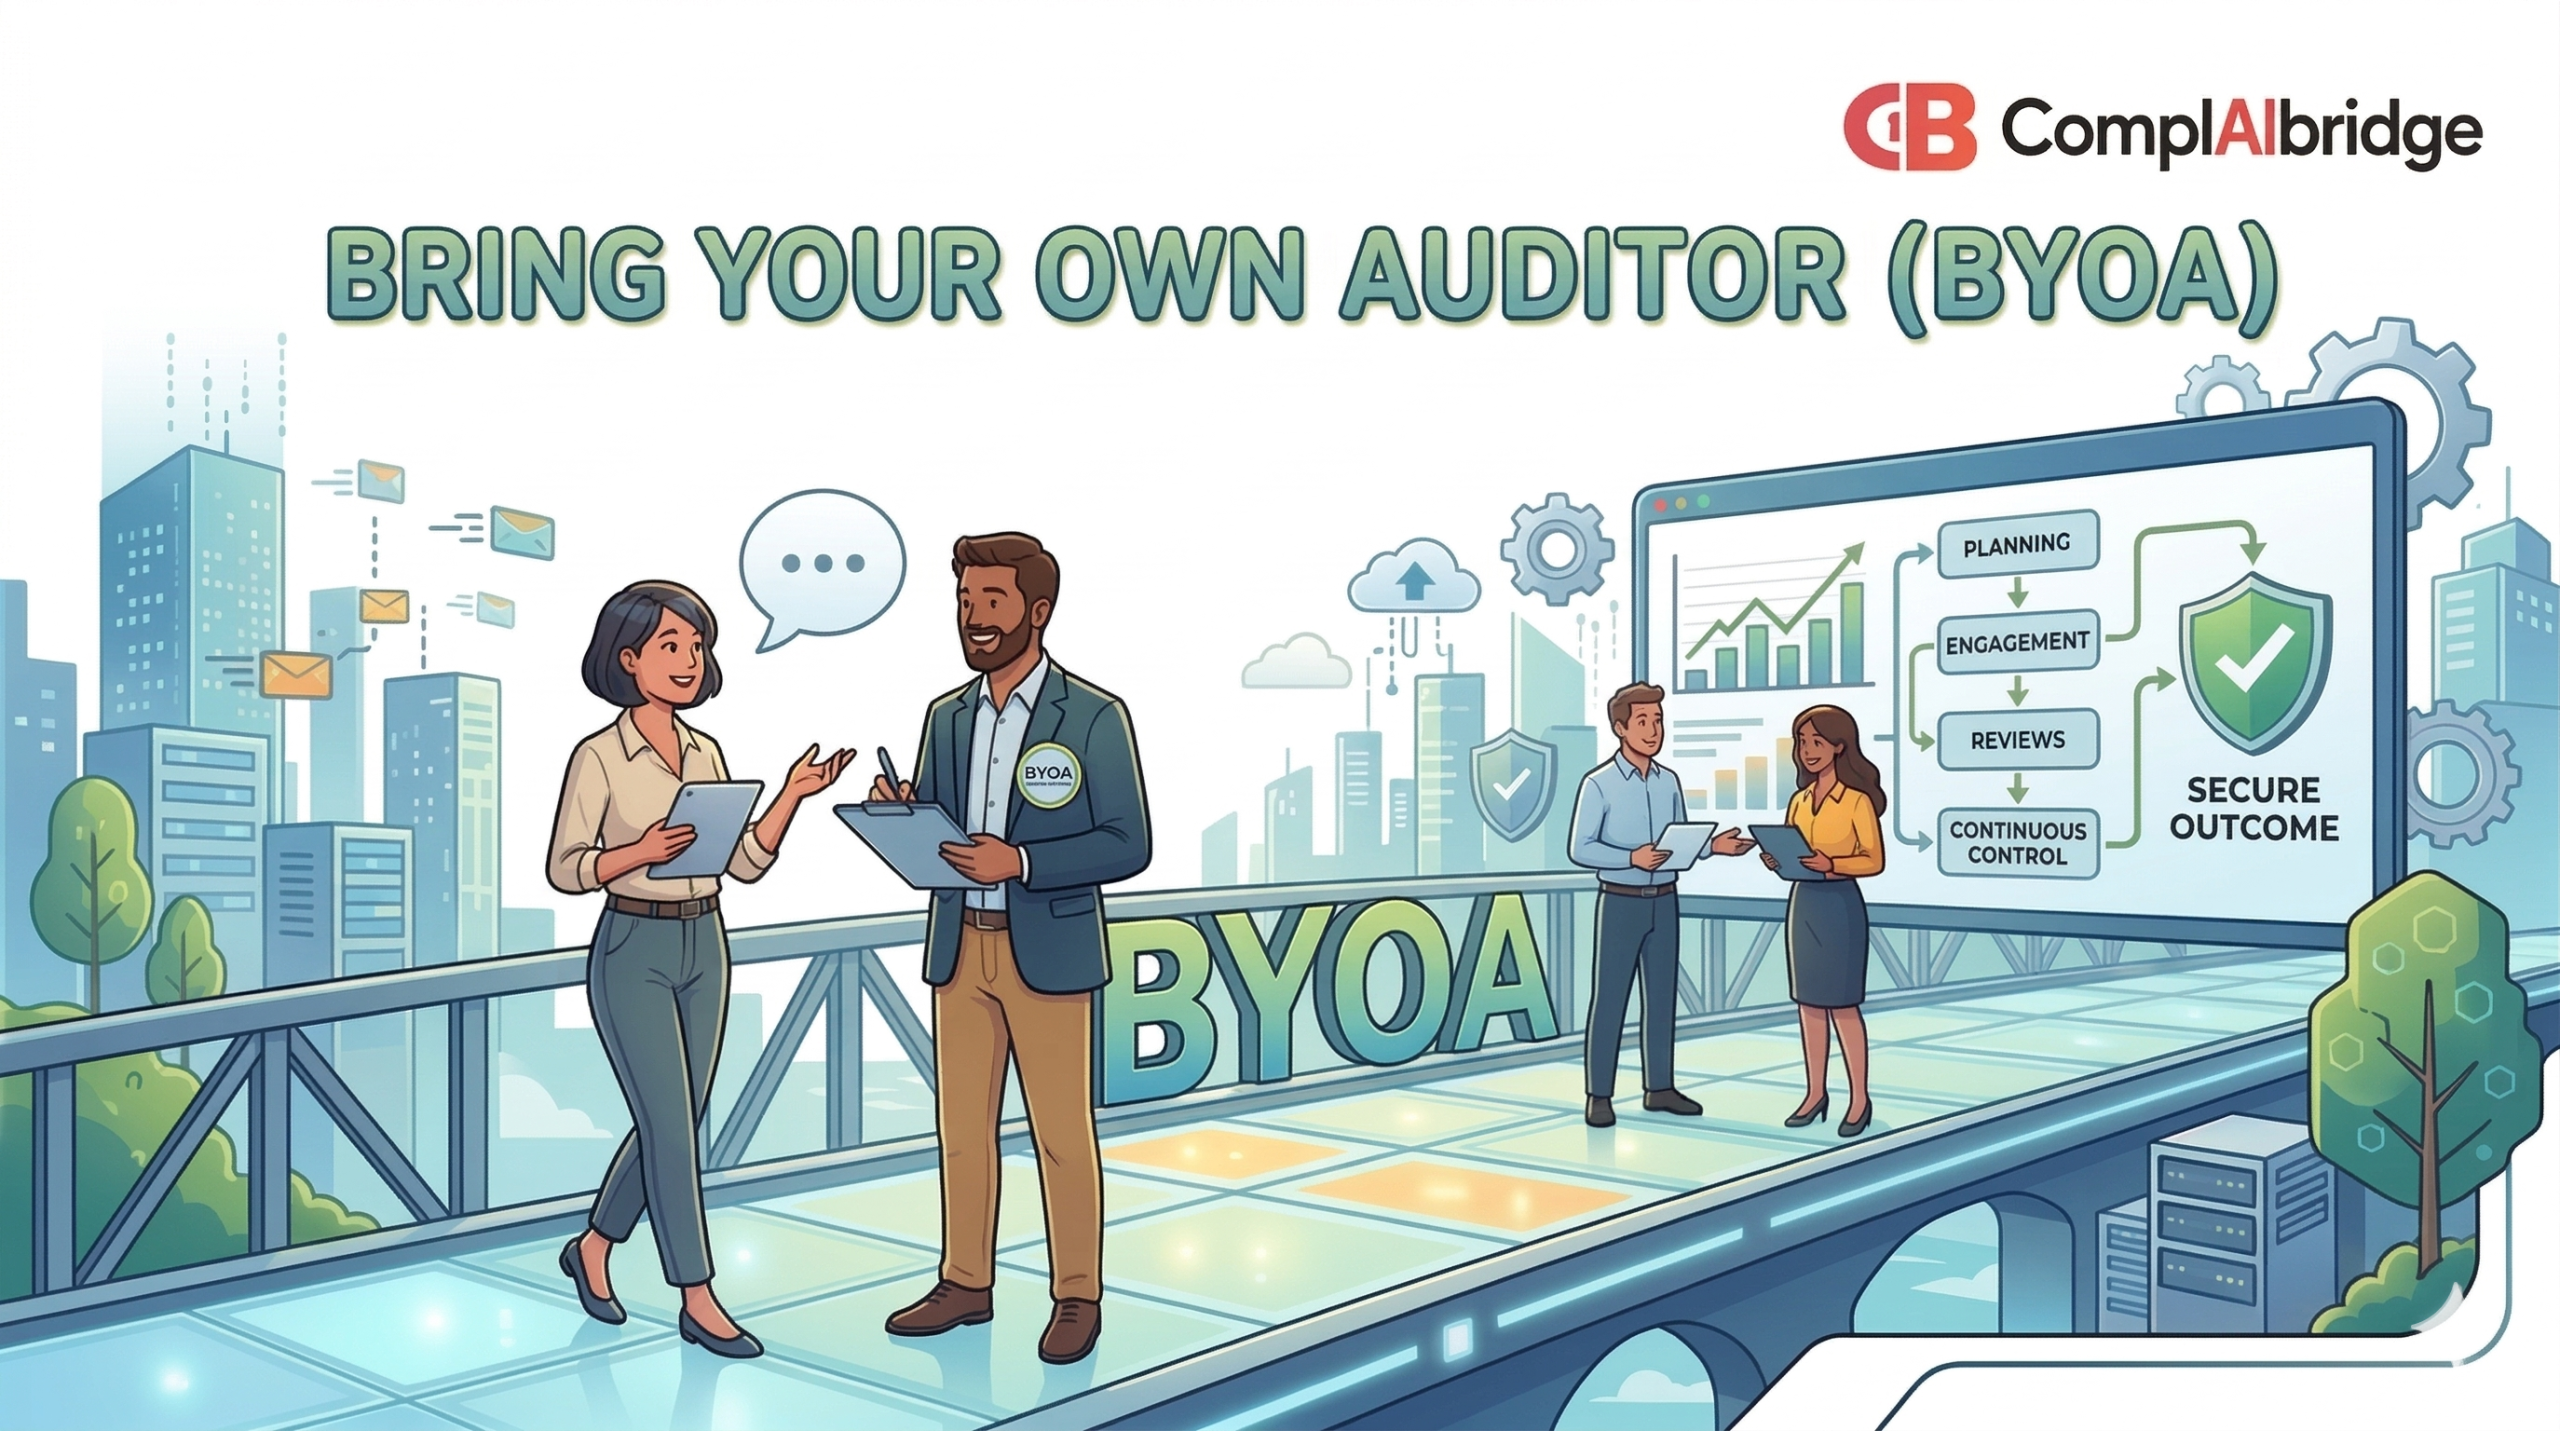
Bring Your Own Auditor (BYOA): Why Auditor Independence Matters More Than Ever
For most organisations, audits are something you prepare for and not something you control. That's where BYOA changes the equation.
 Engineering
DevGovOps: Embedding Governance Into the Speed of Innovation
Software delivery has evolved rapidly over the past decade. Governance, despite being just as critical, has not kept pace.
 Compliance
What Organisations Still Get Wrong About Audit Readiness
Most organisations say they're "audit-ready" right up until the audit actually begins. That's when the familiar patterns emerge.
 Compliance
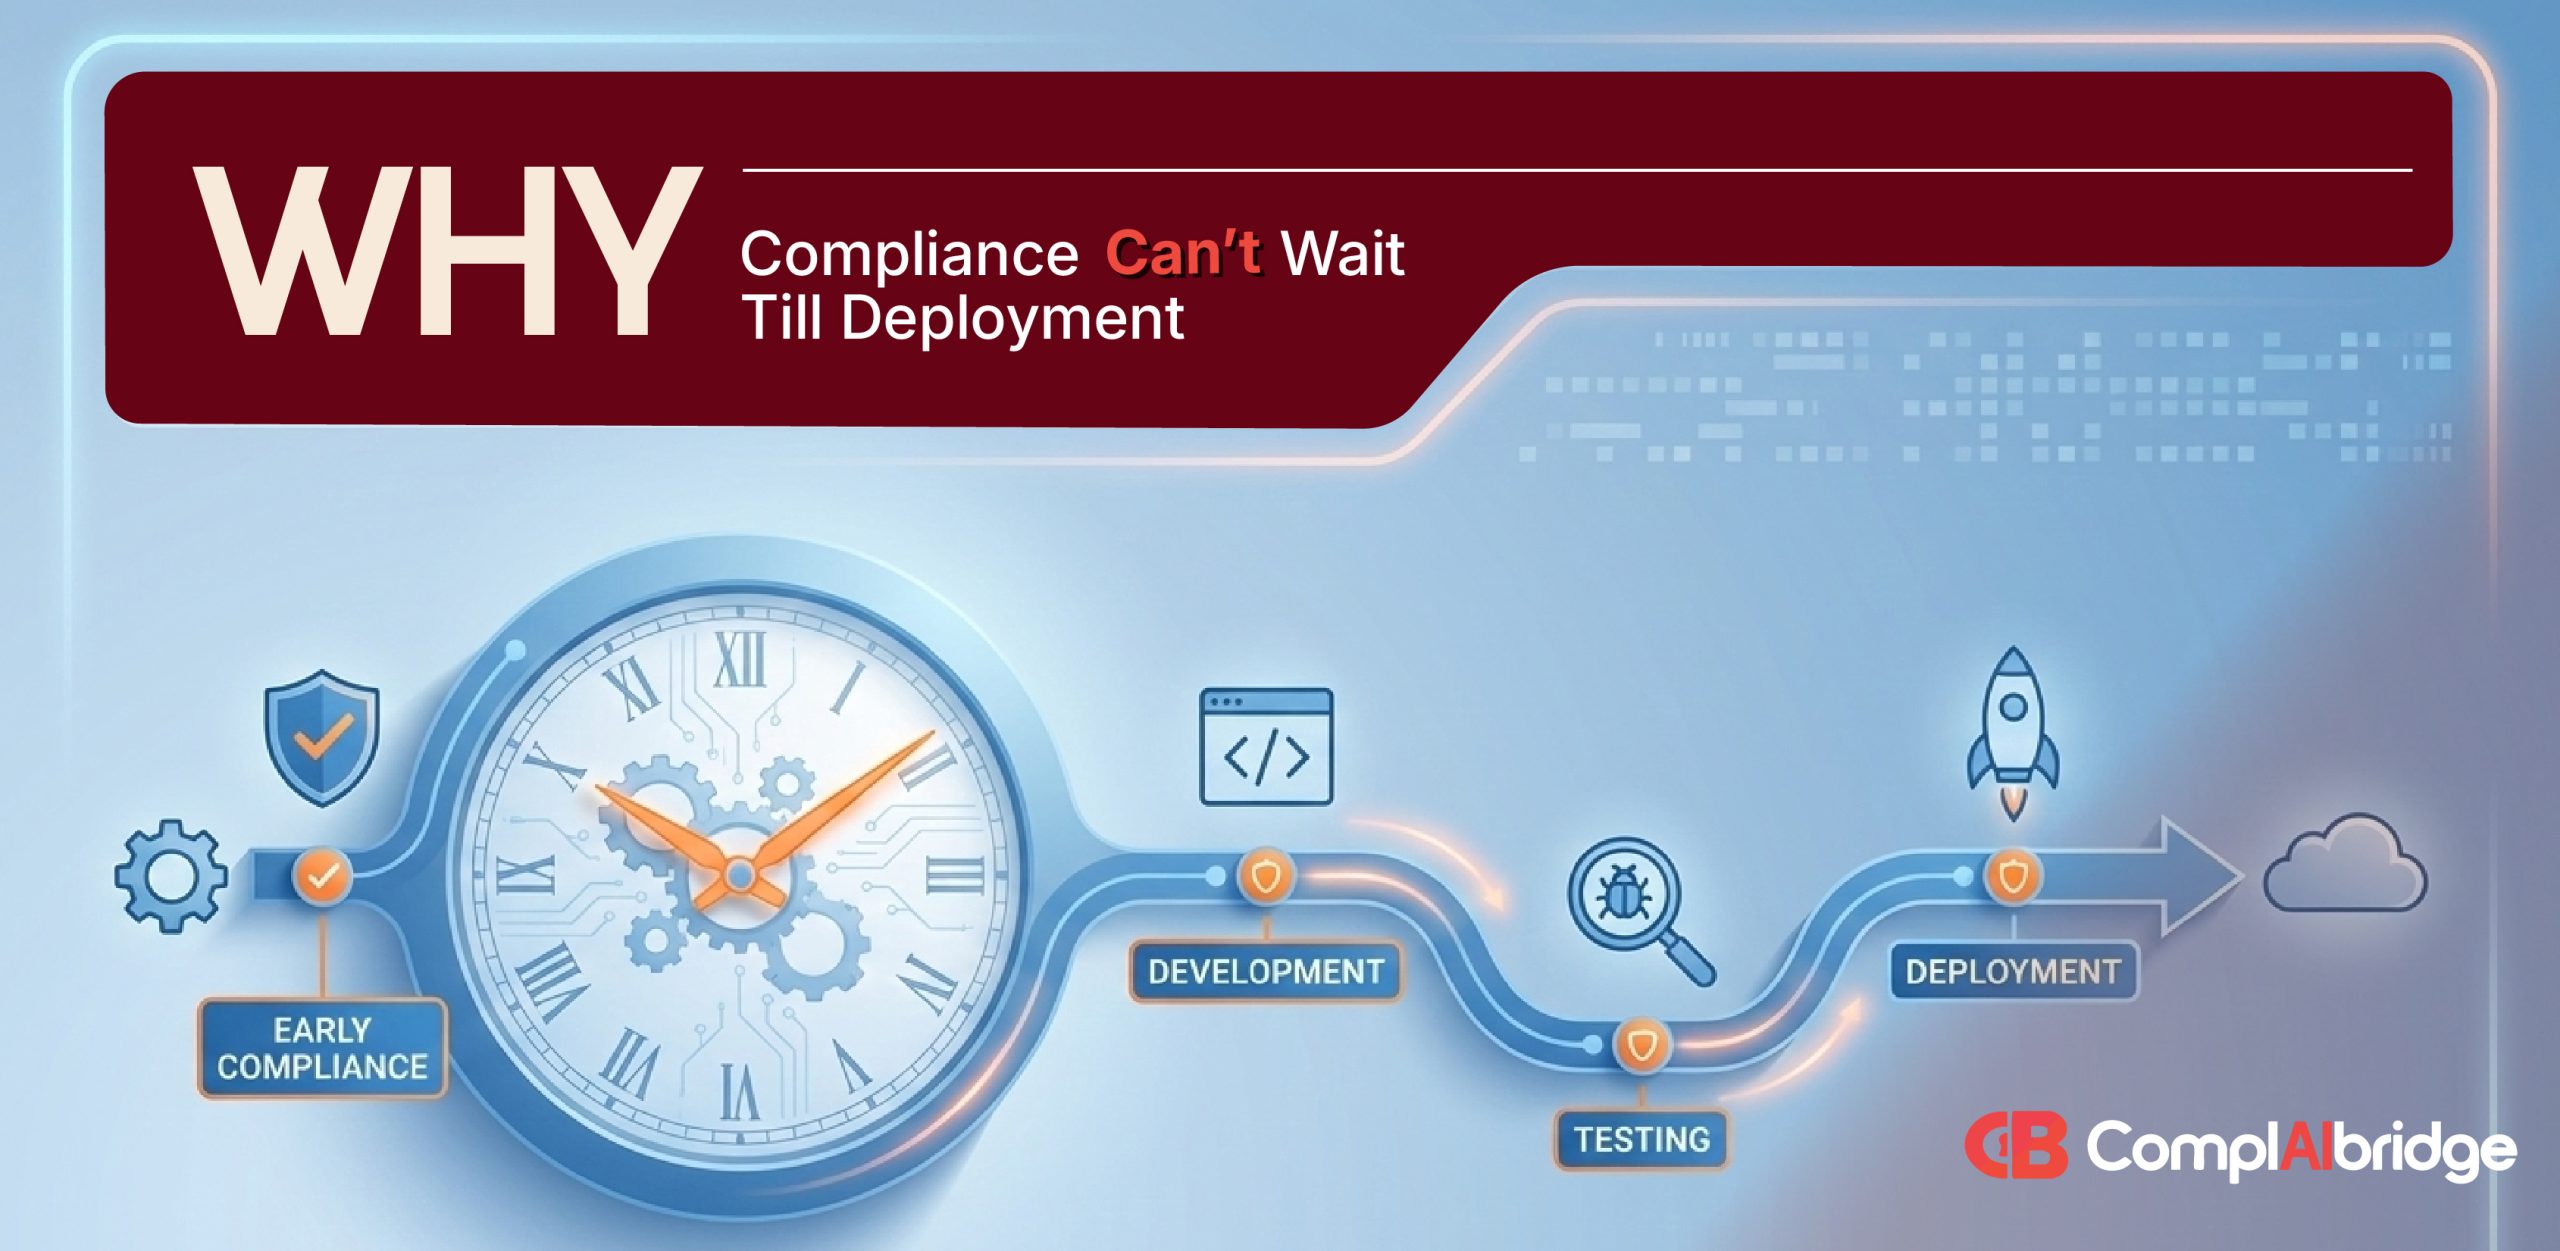
Why Compliance Can't Wait Till Deployment
Build the product. Deploy the system. Then run checks, audits, and controls to make sure everything is "compliant enough." That approach no longer works.
 Insights
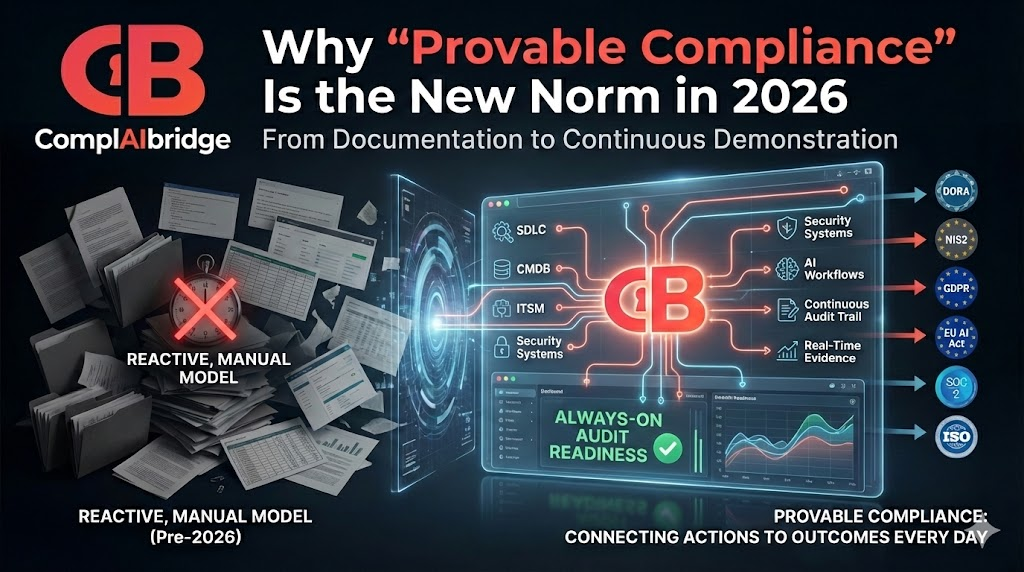
Why "Provable Compliance" Is the New Norm in 2026
For decades, compliance was treated as a documentation exercise. In 2026, that model is officially broken.
 Security
Mapping CVEs and CWEs to Compliance Frameworks Automatically
Security teams are drowning in vulnerability data. Compliance teams are drowning in control requirements.