Blog
Insights on compliance,
AI, and how teams build.
Field notes on shipping compliant software, from classic SDLC to AI-native pipelines.
 Regulatory
DORA Is Changing the Rules of Operational Resilience. Are Teams Ready?
For years, most financial institutions have treated operational resilience as something you prepare for periodically.
 Security
The Cost of Late-Stage Vulnerabilities: Why "Catching It Later" Is So Expensive
A "late stage" vulnerability is any security issue you discover during testing, just before go-live, during an audit, or worse, in production.
 Insights
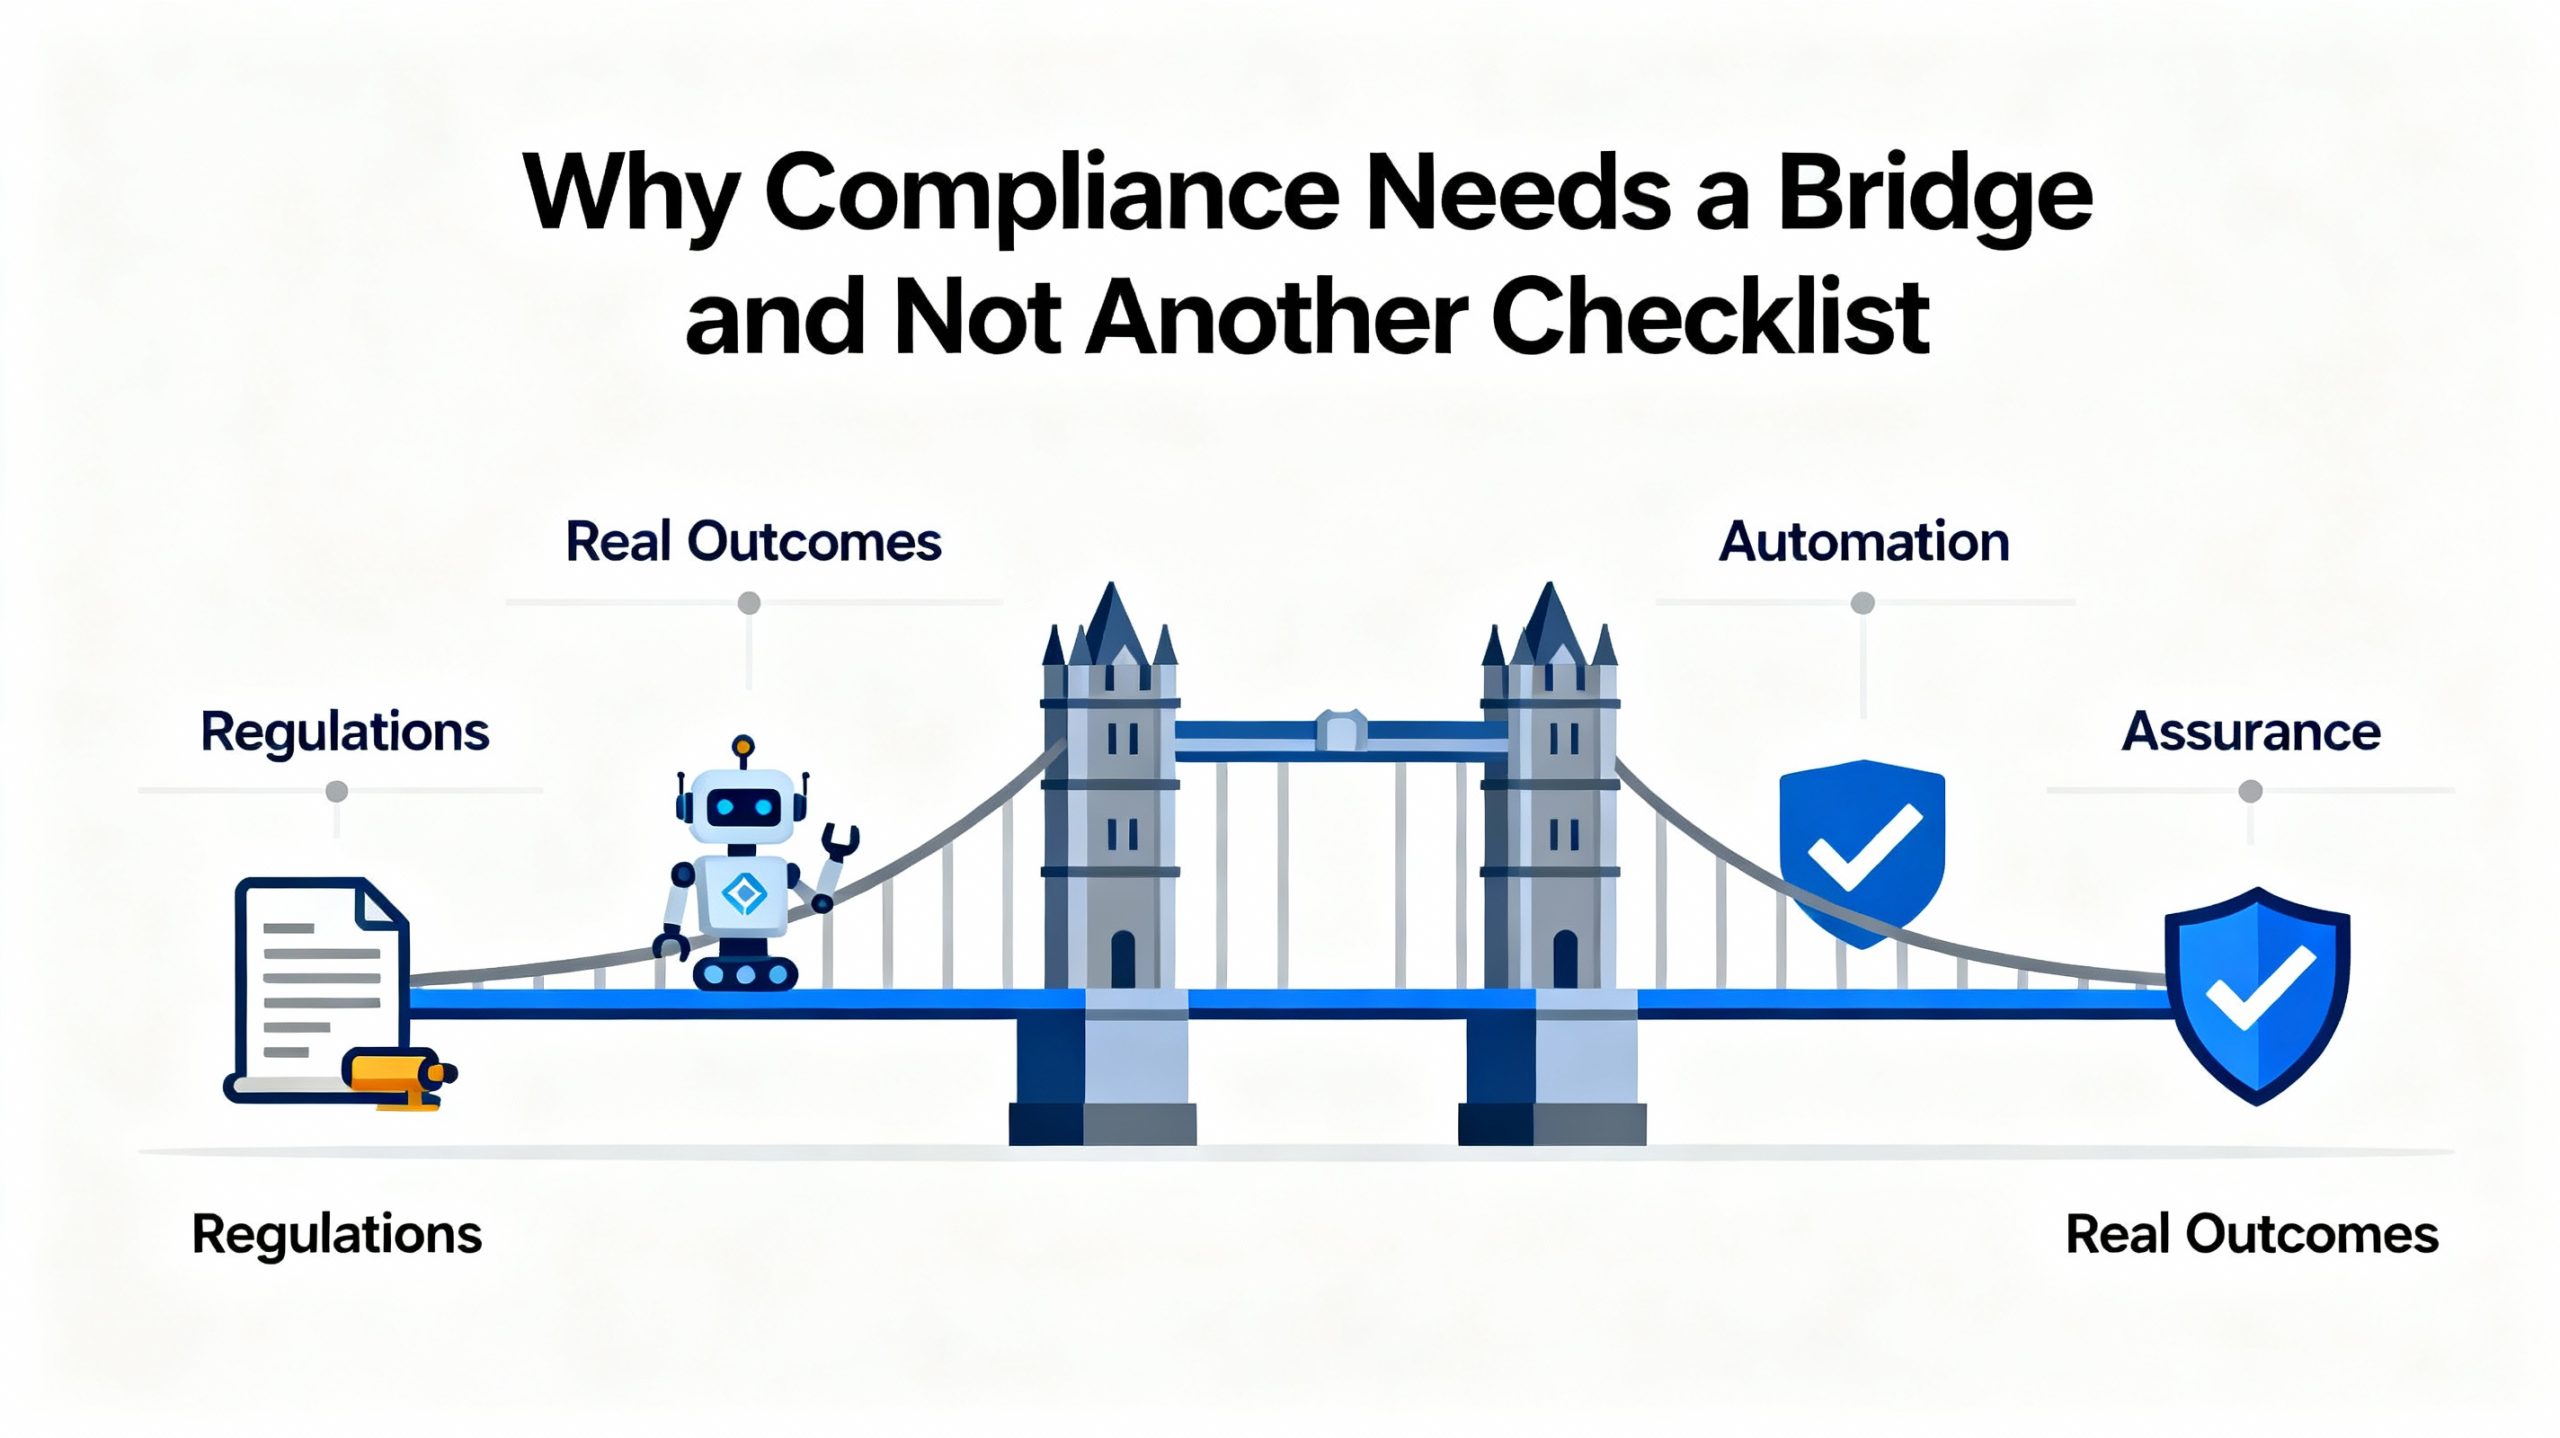
Why Compliance needs a bridge and not another checklist
Even today, for most organizations, compliance still feels like a never-ending loop of forms, audits, and documentation.
 Product
Why Continuous Compliance Needs a Living CMDB
Most organisations have a CMDB (Configuration Management Database). But few actually use it for compliance.